At KARL HUGO, we recognise that cybersecurity is far more than just IT. In an increasingly digital world, it is our responsibility as a company to protect not only our own organisation and employees, but also our customers and partners.
On 8 September 2026, we took the next step with a joint kick-off. Over the coming months, we will systematically strengthen our information security with the long-term goal of achieving: ISO 27001 certification.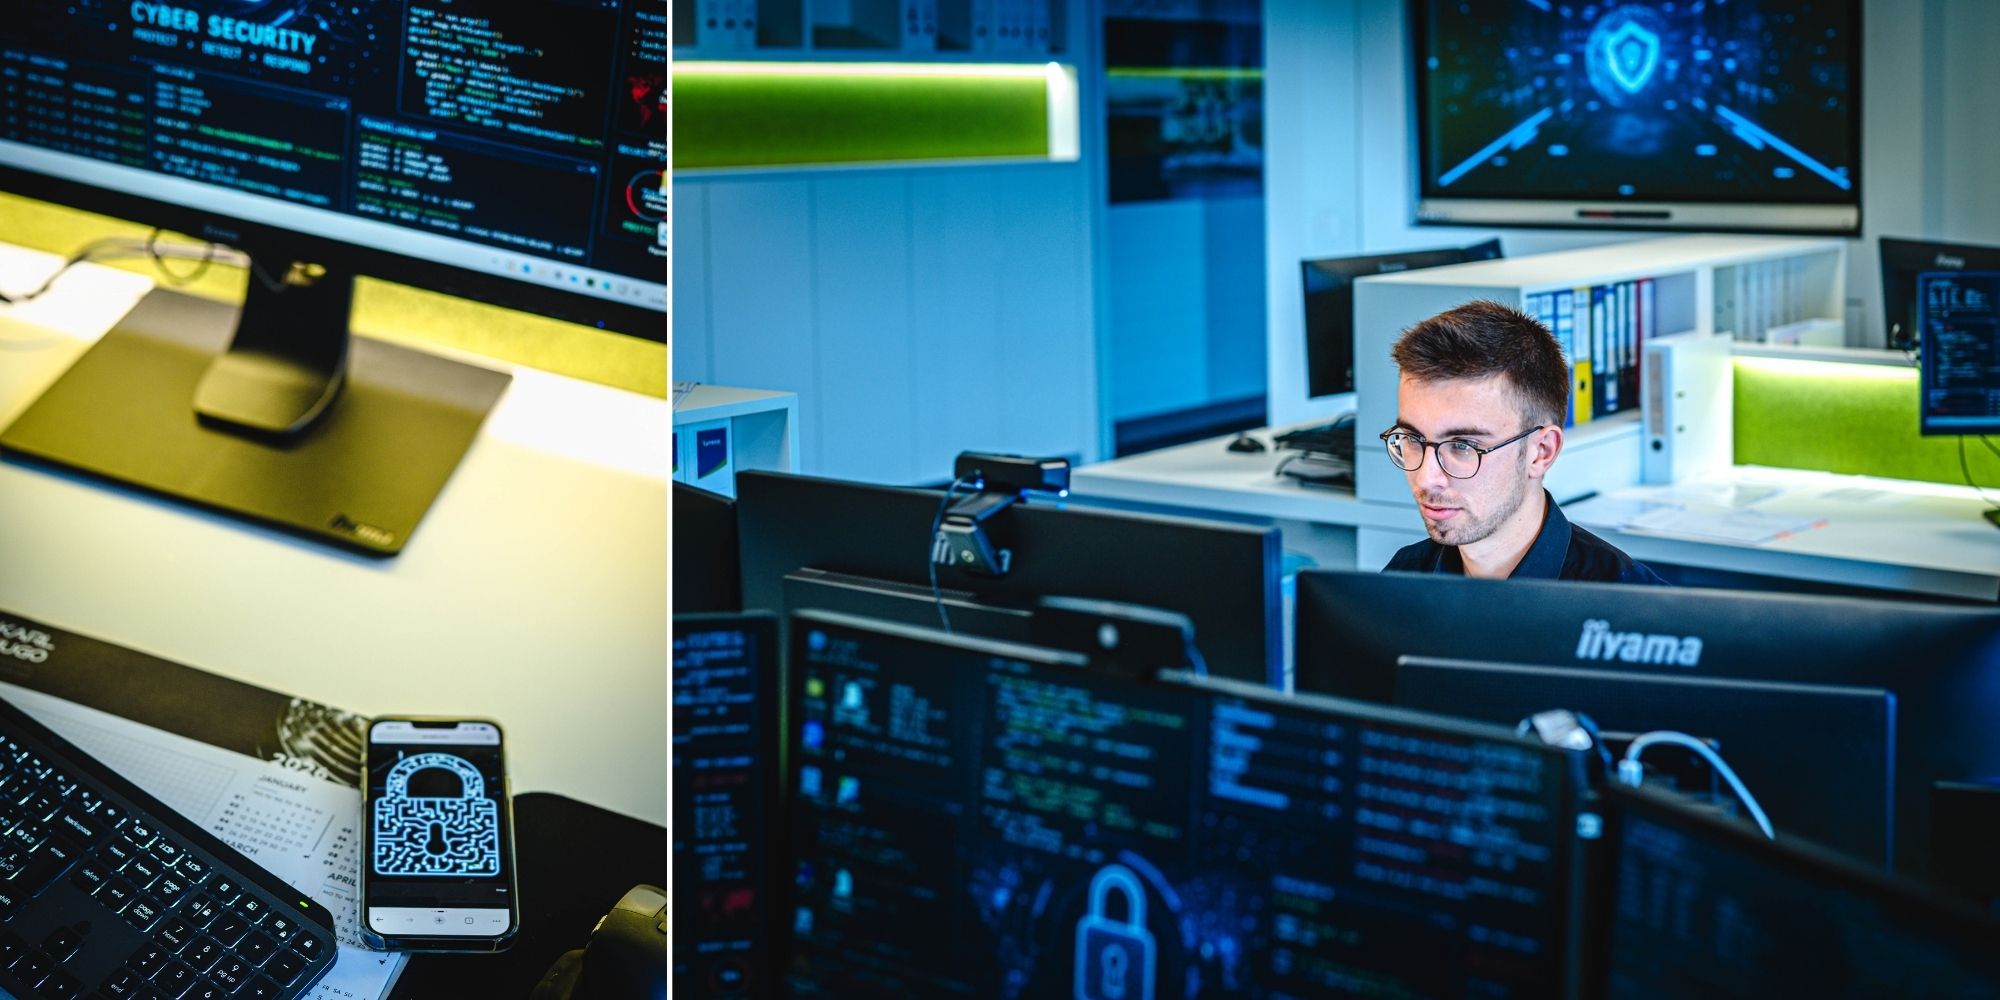
A responsibility that goes beyond our own company
Information security requirements are increasing. New regulatory frameworks, such as the European NIS2 Directive, reflect the growing importance of cybersecurity for businesses. For us, however, it’s more than just meeting these legal obligations.Many of our customers operate in essential sectors: from energy and health to nuclear technology and other sensitive industries. Contributing to these projects also gives our work particular significance.
Our customers need to know that they can rely on us to deliver technically sound, high-quality work and to handle their information, data and projects responsibly. Information security has therefore become an integral part of a reliable industrial partnership.
Trust as the basis of collaboration
We build our relationships with customers, partners and employees on trust and equal collaboration, often developing them over many years or even decades. As digitalisation progresses, this trust takes on an additional dimension in the form of responsible handling of information, systems and access.For us, cybersecurity goes beyond firewalls, software and passwords. It is also about safeguarding the trust on which our relationships are founded.
Technology, processes and people
Technical safeguards alone are not enough. Everyday situations, such as receiving a phishing email, clicking on something without thinking or using an unknown storage device, can pose a security risk. Information security must therefore address technology, internal processes, and how digital information is handled.This includes clearly defined responsibilities and access rights, structured onboarding and offboarding procedures for employees, and the secure handling of passwords, data, and external storage devices.
At KARL HUGO, cybersecurity is not treated as an isolated IT project. We already work with defined and auditable processes through ISO 9001 and ISO 14001. We are now applying this same approach to information security, integrating it into our existing management system.
This is particularly important in an area where risks and threats are constantly evolving. Our processes and measures must evolve accordingly.
Employees as an essential part of information security
Alongside technical and organisational measures, it is crucial that our employees recognise potential risks and understand the necessity of specific security measures.How can I recognise a suspicious email? How should passwords be handled securely? Why can an unknown USB drive pose a risk? What should I do if something seems unusual?
Our aim is to make cybersecurity as practical and relevant to everyday work as possible. At our next annual employee workshop in February 2027, we will dedicate high attention to this topic. Together with experts, we will use practical examples to demonstrate what information security means in day-to-day work.
Our path towards ISO 27001
The kick-off in September 2026 marked the beginning of the project. Over the coming months, we will assess our current position, identify the necessary measures, and integrate the relevant processes and documentation into our existing management system. Following the employee workshop in February 2027, we will develop the system step by step to prepare for the ISO 27001 requirements.Certification is planned for spring 2028. This will coincide with revisions of our existing ISO 9001 and ISO 14001 certifications. This provides a logical opportunity to integrate information security into our integrated management system, managing it according to the same clear, auditable structures that we already apply to quality and environmental management.
Preparing for continued digitalisation
It is impossible to predict every digital challenge that industrial companies will face in the years ahead. However, we can put structures in place today to respond appropriately to new developments and emerging risks.By taking this next step, we are preparing KARL HUGO for these future requirements, and ensuring that our customers, partners, and employees can continue to trust us to handle their affairs responsibly.

